News Vulnerabilities & Zero-Days
curl 8.23.0 fixes High-severity HTTP/2 use-after-free CVE-2026-92392
curl 8.23.0, released on 14 October 2026, fixes CVE-2026-92392, a use-after-free in HTTP/2 uploads that affects curl and libcurl 8.12.0 through 8.22.0. A malicious server can trigger it, and the advisory shows it can be turned into code execution under narrow conditions.
Key takeaways
- CVE-2026-92392 is a High-severity use-after-free in curl's HTTP/2 upload handling.
- It affects curl and libcurl 8.12.0 through 8.22.0, fixed in 8.23.0.
- A malicious server can trigger it; code execution is possible only under narrow conditions.
- Applications that bundle libcurl need to be rebuilt, not just the system curl updated.
- Avoiding HTTP/2 is a temporary mitigation if you cannot upgrade.
The curl project released curl 8.23.0 on 14 October 2026 with a fix for CVE-2026-92392, a use-after-free in HTTP/2 uploads. curl rates it High. It affects curl and libcurl 8.12.0 through 8.22.0, including the command-line tool.
What is the vulnerability? #
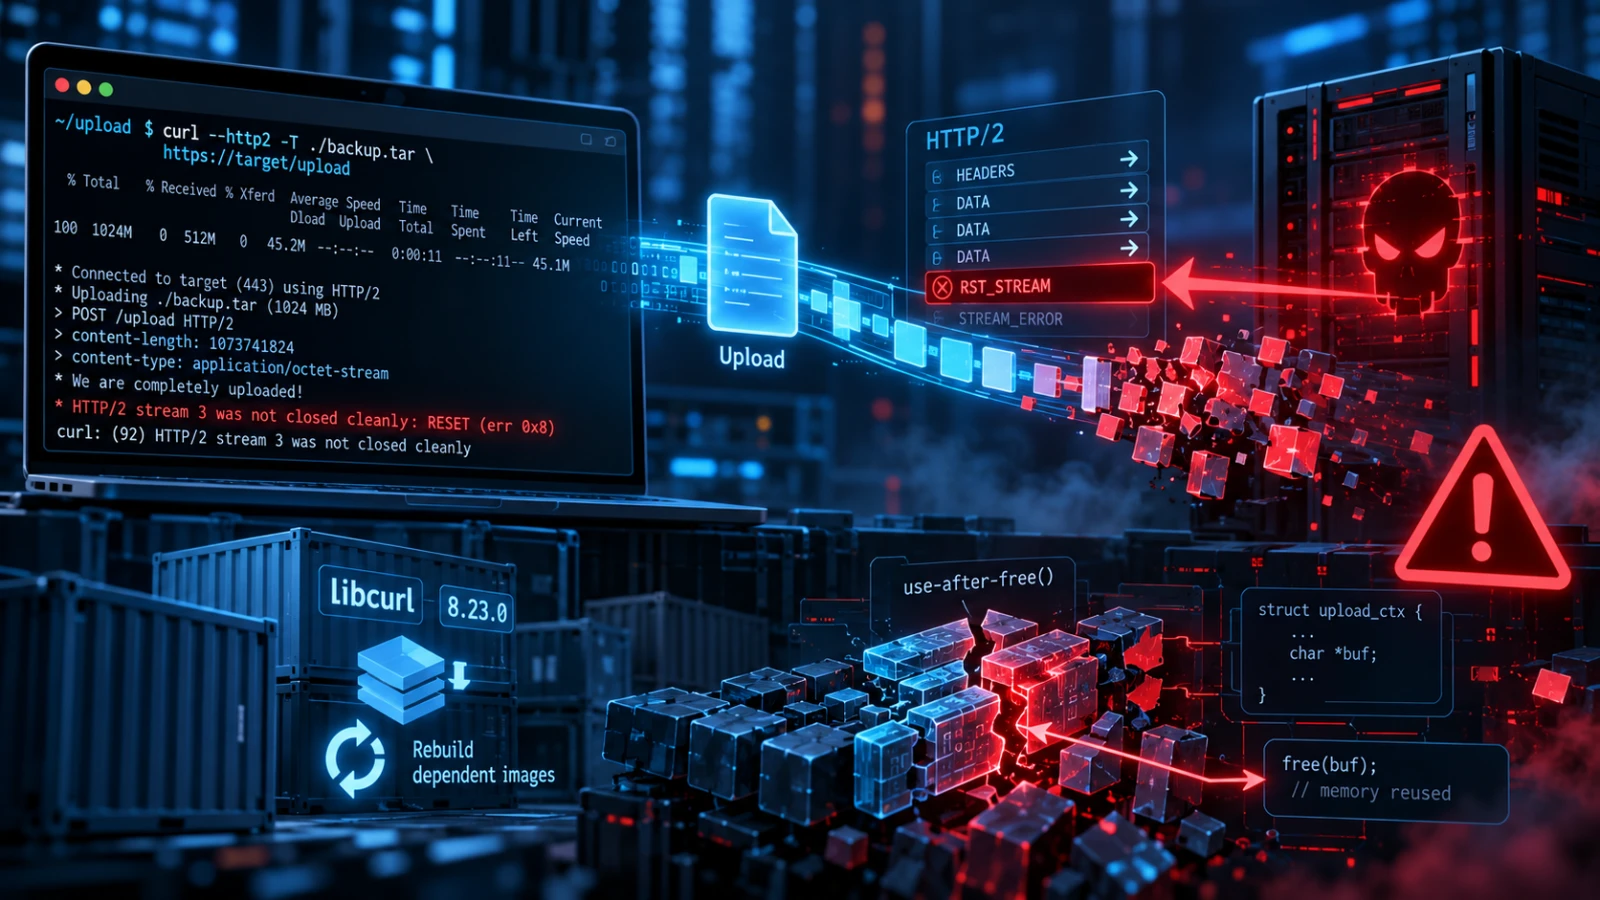
During an upload, curl mishandles an HTTP/2 RST_STREAM from the server with the reason HTTP_1_1_REQUIRED or REFUSED_STREAM, the advisory says. This leads to a use after free of a struct Curl_easy object (CWE-416).
The attacker is a malicious server receiving an upload. The advisory says the flaw has been shown to be convertible to remote code execution, but only when many conditions line up. They include knowing the exact curl version and architecture, a compatible libc allocator and heap layout, specific nghttp2 and TLS 1.3 behaviour, and suitable timing across two parallel transfers. The command an attacker can run is limited to about 23 bytes.
curl maintainer Daniel Stenberg wrote that "the most likely outcome of an attempted attack is rather just a crash", The Hacker News reported.
Which versions are fixed? #
| Branch | Fixed in |
|---|---|
| Current | 8.23.0 |
| 8.20.x | 8.20.2 |
| 8.16.x | 8.16.2 |
| 8.14.x | 8.14.3 |
Versions before 8.12.0 are not affected. Linux distributions ship their own patched packages, so check your distribution's tracker; for example, Debian 12 is listed as not affected, The Hacker News reported.
Who found it? #
The advisory credits "Luna with Claude (Anthropic)" for the report and Stefan Eissing for the patch. The flaw was reported to the curl project on 15 September 2026 and fixed in coordination with the advisory. A proof of concept became public with the release.
What should developers and operators do? #
- Upgrade to curl 8.23.0, or to the fixed release on your branch.
- If you ship libcurl inside an application or container image, rebuild with the fixed version. Updating the system curl does not update a bundled copy.
- If you cannot upgrade yet, the advisory suggests avoiding HTTP/2, for example with
--http1.1or by settingCURLOPT_HTTP_VERSIONtoCURL_HTTP_VERSION_1_1.
Sources
- curl security advisory for CVE-2026-92392, curl
- Report on the curl fix and proof of concept, The Hacker News
Questions this raises
- Am I affected if I only download files with curl?
- The flaw is in the HTTP/2 upload path, triggered by a malicious server receiving an upload. Upgrading is still the safest option.
- Is it being exploited?
- The advisory does not report exploitation in the wild. A proof of concept was made public with the fix on 14 October 2026.
- What if I cannot upgrade right away?
- The curl advisory suggests avoiding HTTP/2, for example with --http1.1, until you can upgrade or apply the patch.
VulnerabilityOpen Source SecurityApplication SecuritySecurity Updatecurl