News Vulnerabilities & Zero-Days
Docker Hub flaw let users act as others in the registry for two years
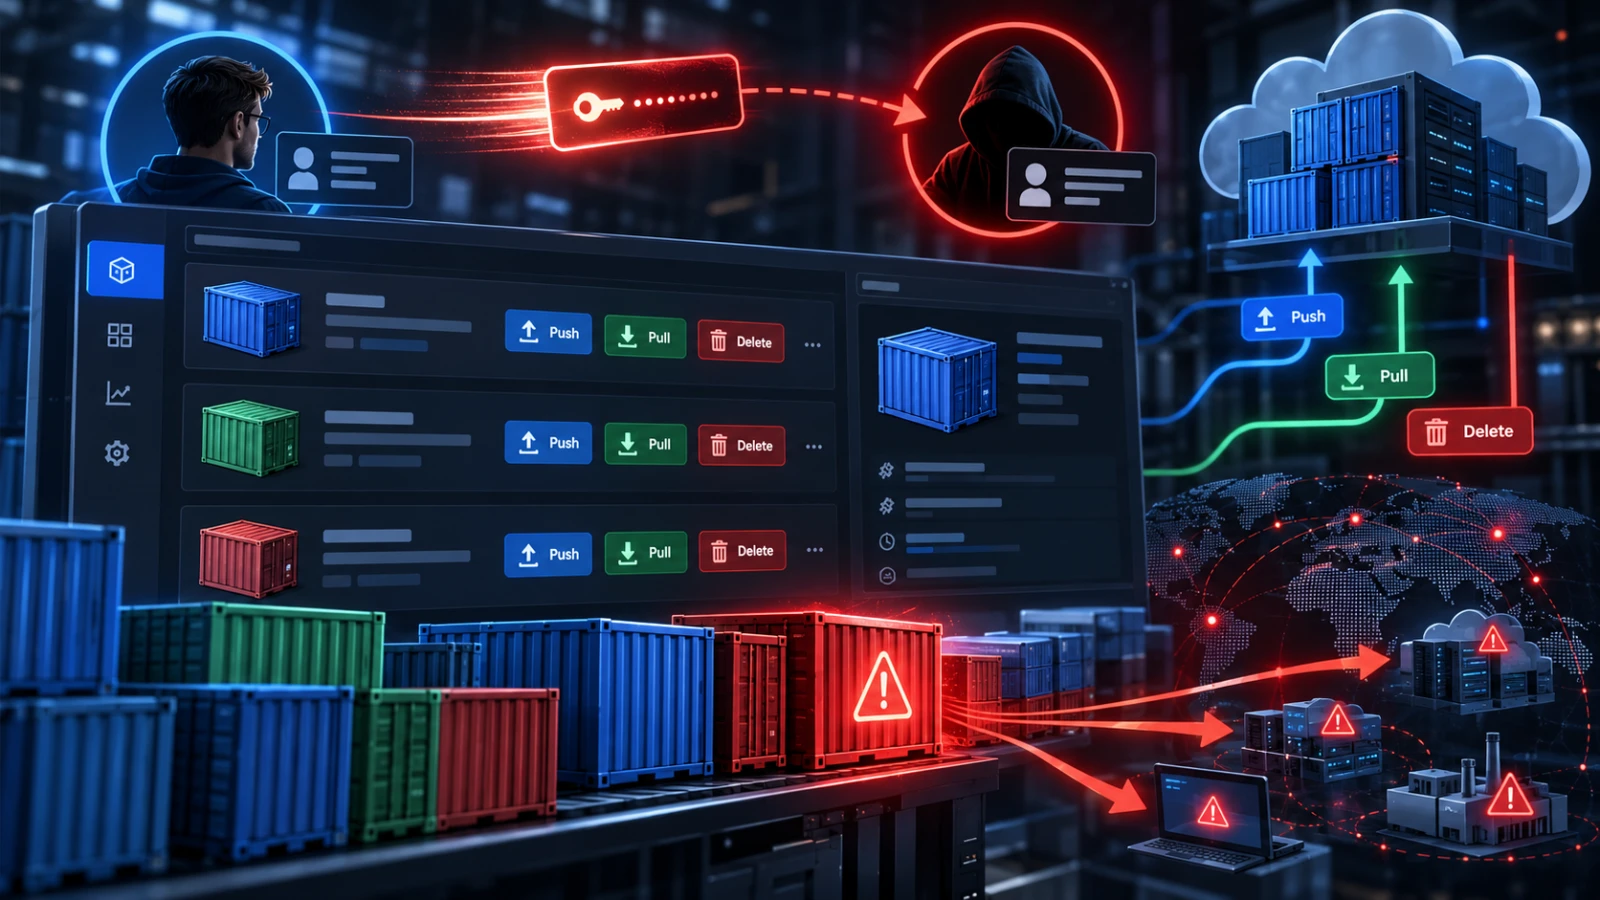
Docker fixed CVE-2026-105445, a critical Docker Hub flaw that let a user push, pull or delete images as another user by abusing account-to-organization conversion. Docker says it found no evidence of exploitation and has deactivated the affected tokens.
Jaydeep Bhatt