News Cyber Attacks
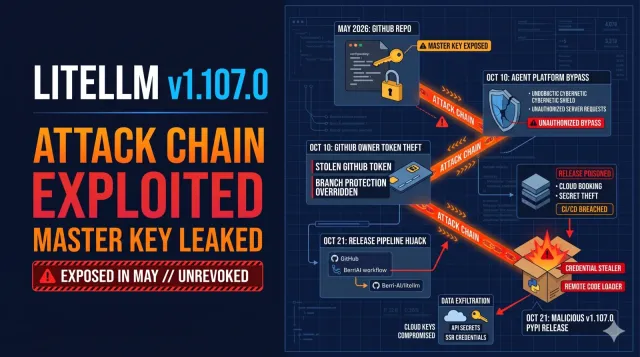
One Forgotten Key: LiteLLM Traces Malicious 1.107.0 Release to a Master Key Leaked on GitHub in May
LiteLLM's root-cause analysis says a master key accidentally committed to a public repository in May, and never revoked, handed the attacker a GitHub organization owner's token. From there, stolen maintainer tokens were used to build, approve and publish a backdoored release, then wipe the evidence.
Jay B.