News Vulnerabilities & Zero-Days
Low Score, Big Cover-Up: China-Nexus Warp Panda Used a 2.7-Rated VMware ESX Logging Flaw as a Zero-Day
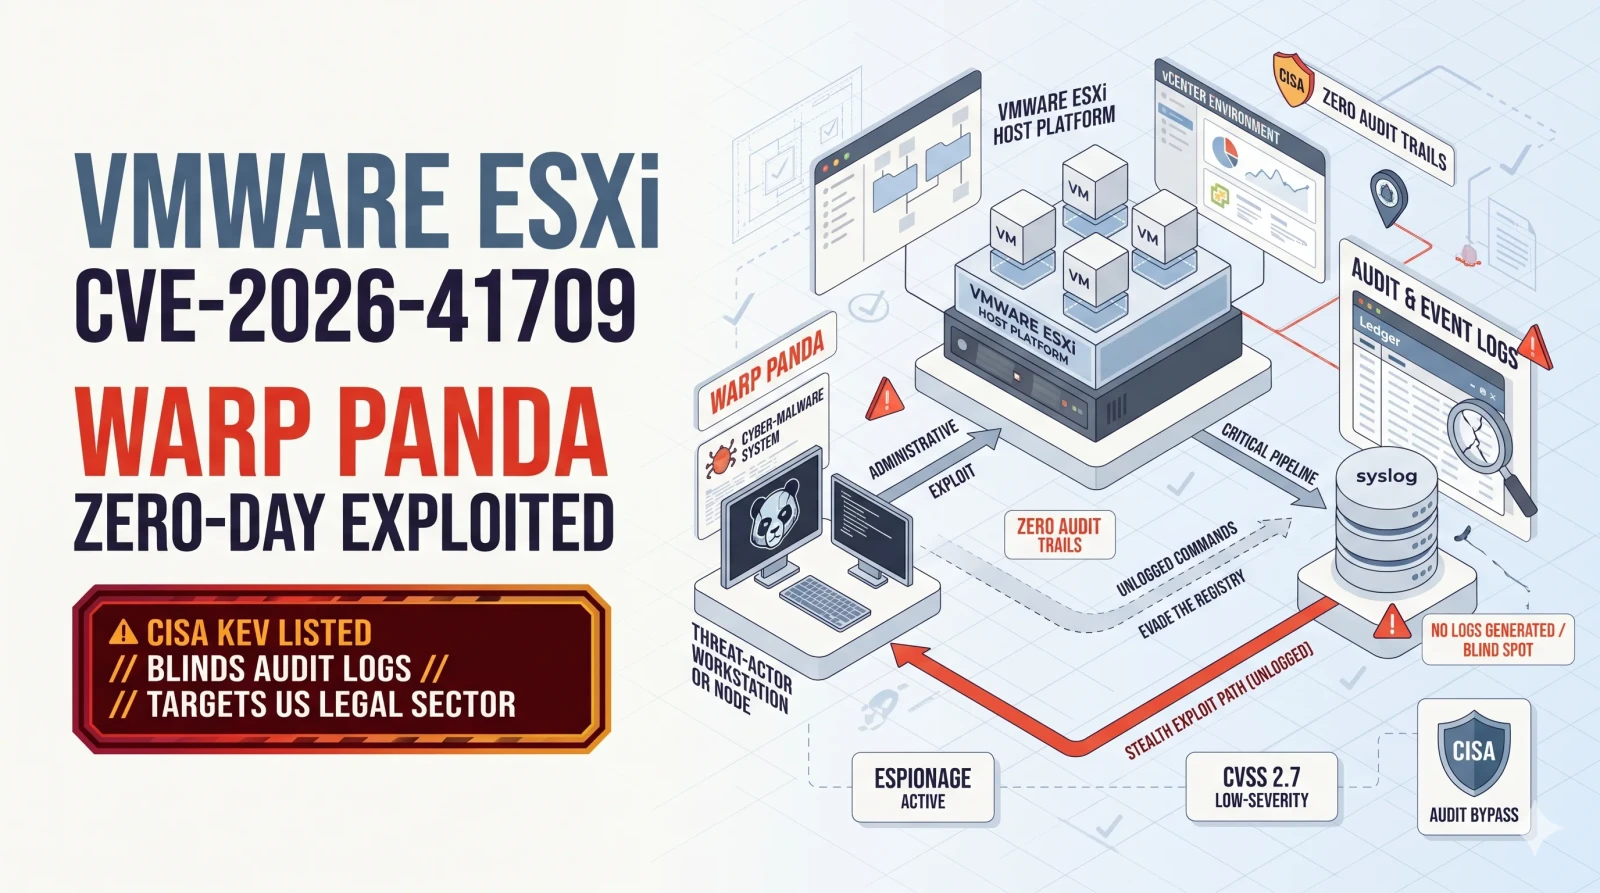
CrowdStrike says China-nexus group WARP PANDA exploited CVE-2026-41709, a low-severity ESX command logging bypass, as a zero-day in several intrusions. CISA has added the flaw to its Known Exploited Vulnerabilities catalog with a November 11 deadline.
Key takeaways
- CrowdStrike says China-nexus WARP PANDA exploited VMware ESX flaw CVE-2026-41709 as a zero-day in several cases, as late as early 2026.
- The bug, rated CVSS 2.7, lets a malicious administrator perform some operations without them being logged.
- Broadcom fixed it on July 29, 2026 in VMSA-2026-0006; CISA added it to KEV on October 28 with a November 11 deadline.
- CrowdStrike says the group targeted US entities, including in the legal sector, and deployed malware in vCenter environments.
- The same Broadcom advisory also fixes critical vCenter flaws rated 9.8, so unpatched hosts face wider risk.
A VMware ESX bug rated just 2.7 out of 10 has turned out to be useful to a Chinese espionage group: it let them work on hypervisors without leaving a trail.
CrowdStrike said in its 2026 legal sector threat report, published October 28, that the China-nexus adversary it tracks as WARP PANDA exploited CVE-2026-41709 as a zero-day "in several cases," as late as early 2026. The US Cybersecurity and Infrastructure Security Agency (CISA) added the flaw to its Known Exploited Vulnerabilities (KEV) catalog on October 28, according to Help Net Security and Cyber Security News, giving federal civilian agencies until November 11 to fix it.
What is CVE-2026-41709? #
Broadcom disclosed and fixed the flaw on July 29, 2026 in advisory VMSA-2026-0006, alongside several more severe VMware bugs.
| Detail | Value |
|---|---|
| Product | VMware ESX (also VMware Cloud Foundation and Telco Cloud Platform) |
| Weakness | Insufficient logging |
| CVSS v3 | 2.7 (Low) |
| Impact | A malicious administrator could perform some operations without them being logged |
| Reported by | Ian Barton, CrowdStrike |
| Workaround | None |
The flaw cannot be used to break in. An attacker needs administrator access first. CrowdStrike describes it as an "ESXi command logging bypass," and Help Net Security, citing CrowdStrike, says it significantly reduced audit trail visibility and helped the group cover its tracks.
Broadcom's advisory does not mention active exploitation.
Who is WARP PANDA? #
CrowdStrike lists WARP PANDA among the top China-nexus adversaries targeting the legal sector, alongside TITAN PANDA, MURKY PANDA and OVERCAST PANDA. It says the group deployed several forms of malware in victims' VMware vCenter environments during multiple intrusions at US-based entities, including targets in the legal sector. CrowdStrike does not name the victims.
Why does a "low" CVSS score matter here? #
Severity scores measure a bug on its own. They do not capture what it is worth to an attacker who already has a foothold. For an espionage group living inside hypervisors, a way to run commands that never reach the logs is valuable: it hides activity from incident responders and makes intrusions harder to scope. This case is a reminder that KEV status, not CVSS alone, should drive patch priority.
Which versions fix CVE-2026-41709? #
| Product line | Fixed build |
|---|---|
| ESX 9.1.x | ESXi-9.1.0.0-25370933 |
| ESX 9.0.x | ESXi-9.0.2.0100-25595025 |
| ESX 8.0 | ESXi80U3j-25429389 |
| VMware Cloud Foundation 5.x | 5.2.4 |
| Telco Cloud Platform 5.0.x and 5.1.x | See Broadcom KB449886 |
The same advisory also fixes two critical vCenter flaws rated 9.8, CVE-2026-59309 and CVE-2026-59310, and a 9.3-rated ESX flaw, CVE-2026-47876, so unpatched hosts carry more risk than the logging bug alone.
What should VMware administrators do? #
- Patch ESX now. Apply the fixed builds above and the rest of VMSA-2026-0006, which also covers critical vCenter bugs.
- Don't rank by CVSS alone. Prioritize anything on the CISA KEV list, regardless of score.
- Hunt on hypervisors. Look for unexplained administrative changes, new accounts and unusual vCenter activity since early 2026, and compare host state with logs.
- Send logs off-host. Forward ESX and vCenter logs to a central, tamper-resistant system so local gaps are easier to spot.
- Lock down admin access. Restrict ESX and vCenter management interfaces to dedicated admin networks with strong MFA.
Sources
- CrowdStrike 2026 Legal Threat Landscape Report, CrowdStrike
- Broadcom advisory VMSA-2026-0006, Broadcom
- CISA adds two known exploited vulnerabilities to catalog (Oct 28), CISA
- Chinese hackers used VMware ESX zero-day, Help Net Security
- CISA warns of VMware ESX logging vulnerability exploited in attacks, Cyber Security News
Questions this raises
- What is CVE-2026-41709?
- It is an insufficient logging flaw in VMware ESX, rated CVSS 2.7, that lets a malicious administrator perform some operations without them being logged. Broadcom fixed it on July 29, 2026.
- Who exploited CVE-2026-41709?
- CrowdStrike attributes zero-day exploitation to WARP PANDA, an adversary it describes as China-nexus, in several intrusions at US-based entities, including targets in the legal sector.
- Can attackers use this flaw to break into ESX?
- No. It requires administrator access. Its value to attackers is hiding what they do after they already have privileged access.
- What is the CISA deadline?
- CISA added the flaw to its Known Exploited Vulnerabilities catalog on October 28, 2026, and US federal civilian agencies must remediate it by November 11, 2026.
VMwareZero-DayCISA KEVCyber EspionageThreat IntelligencePatch Management