News Cyber Attacks
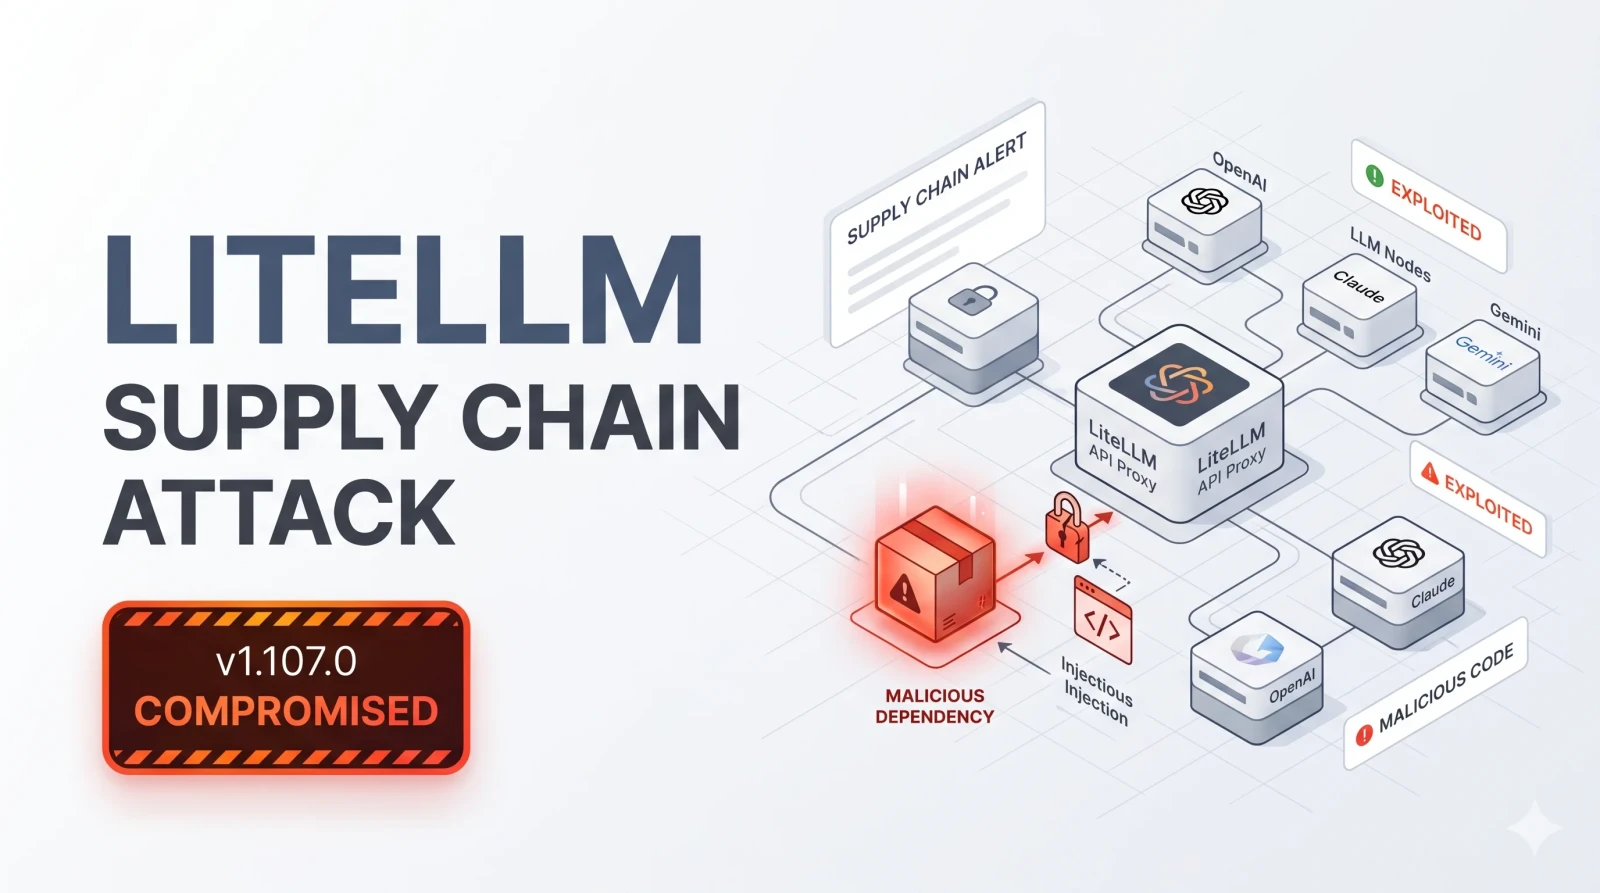
LiteLLM hijacked: poisoned PyPI and Docker release planted credential-stealing malware in popular AI gateway
Attackers used stolen GitHub tokens to publish a malicious LiteLLM 1.107.0 to PyPI and Docker on 21 October 2026. The malware steals cloud credentials, AI provider API keys and secrets, and LiteLLM says anyone who ran it should assume data was taken.
Jay B.